Browse knowledge streams
Web security best practices
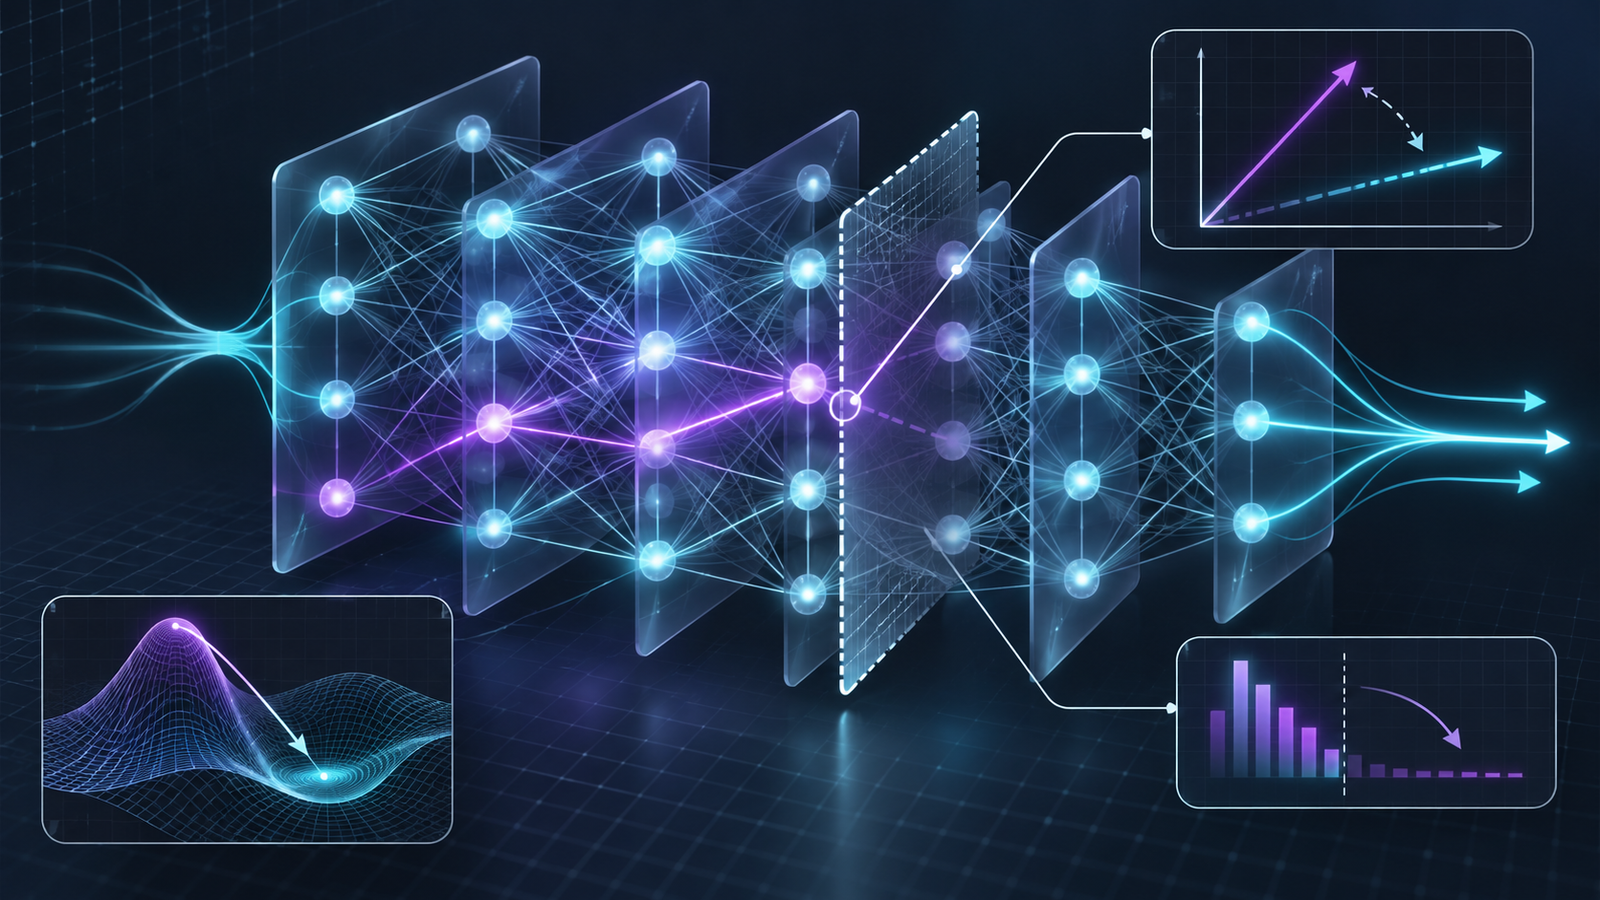
An abliterated LLM is an open-weight model modified to reduce learned refusal behavior. Learn how abliteration works, what the research shows, its limitations, and the security implications for developers.
DeepStateAI
Nov 16, 2026
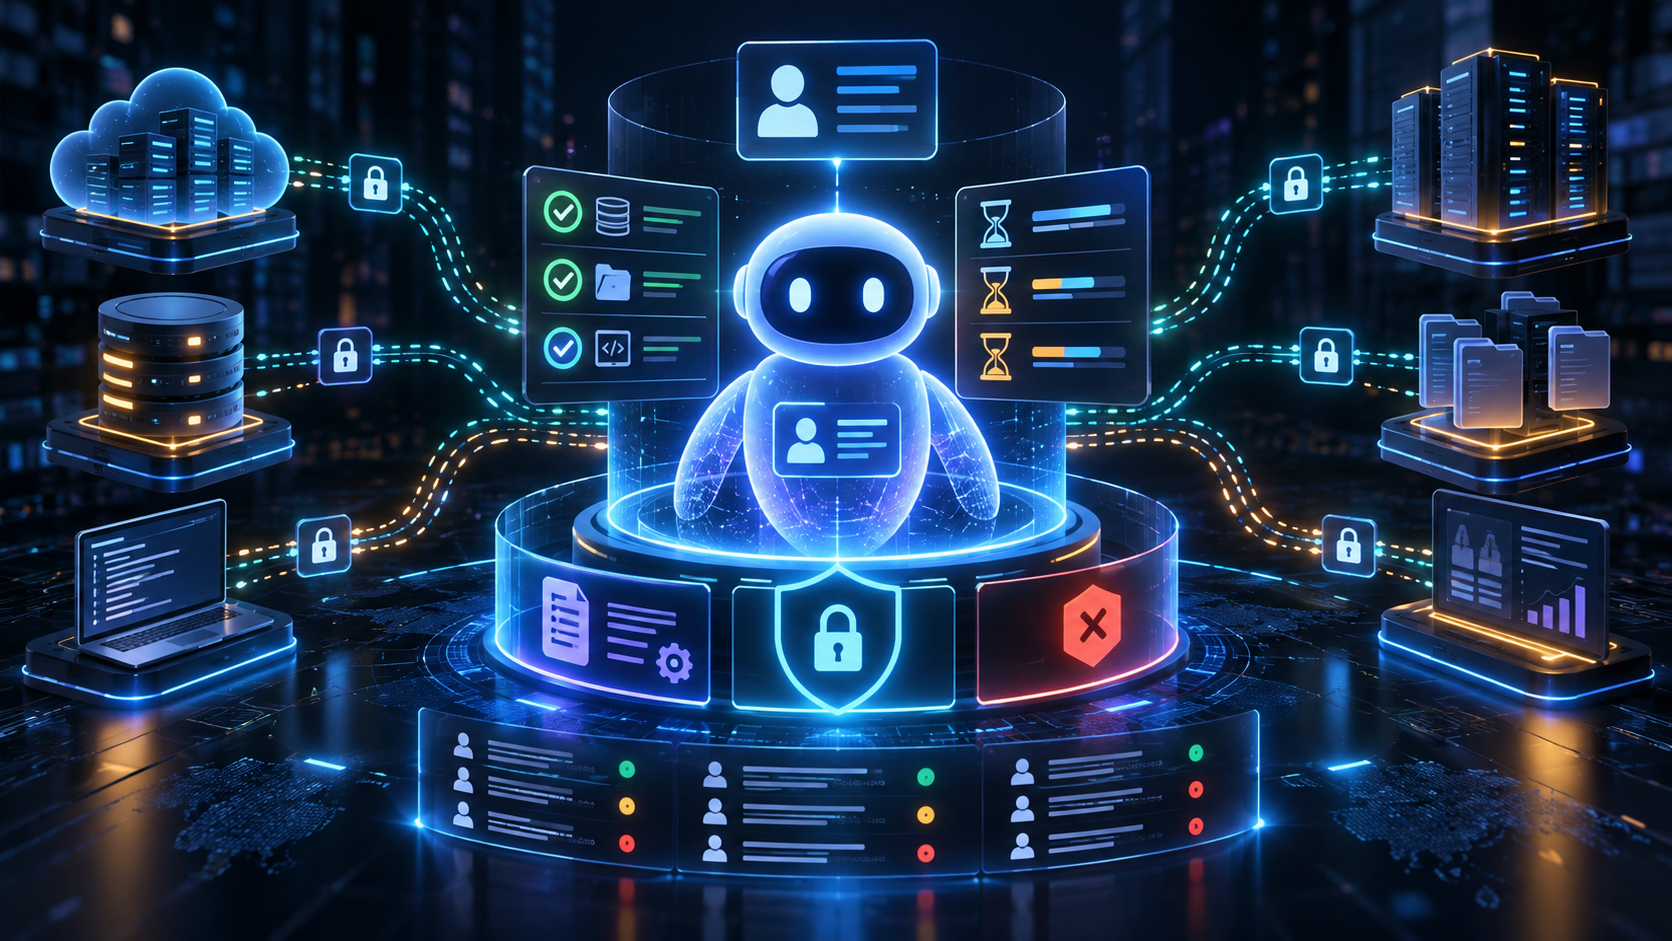
AI agents are moving from answering questions to calling APIs, accessing data and changing systems. The next engineering challenge is not just model safety—it is giving every agent a distinct identity, scoped authority, short-lived credentials and auditable actions.
Sep 24, 2026
As enterprises embed large language models into automation, compliance, and platform engineering workflows, security becomes a trust-boundary problem—not a tooling choice. This article examines the real trade-offs between running local LLMs for data isolation and using public LLMs with carefully secured context, drawing on production architecture patterns, operational risks, and regulatory realities that engineering teams face today.
ControlPlane
Feb 01, 2026